

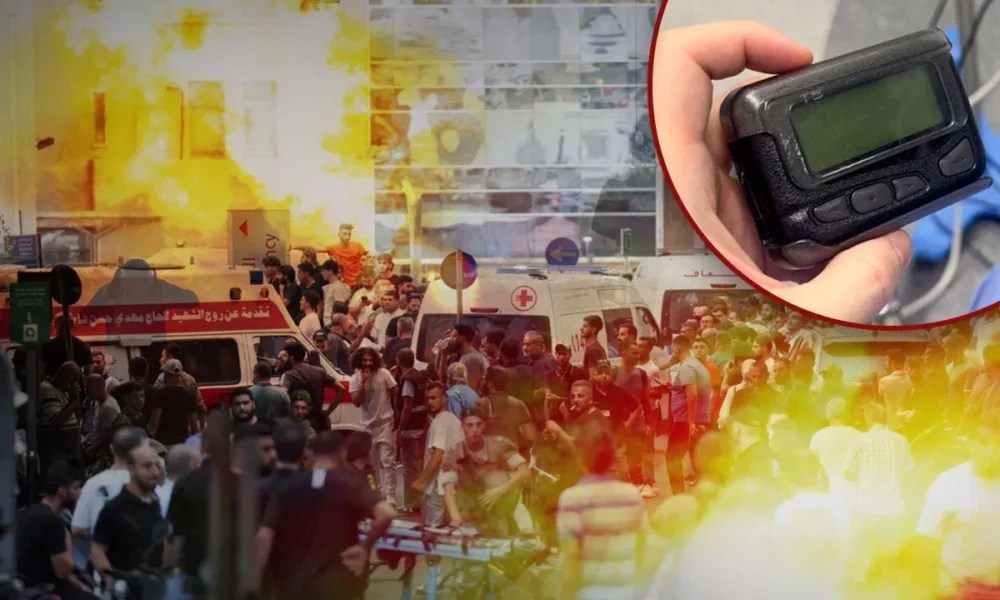
Cybersecurity Crisis: The Pager Explosion in Lebanon Highlights Dire Risks in Consumer Electronics
In a chilling reminder of how vulnerable our consumer electronics can be to cyber threats, the recent explosion of compromised communication pagers in Lebanon has revealed the alarming potential for devices to be weaponized. This harrowing incident occurred in September 2024, when over 21 Hezbollah operatives were killed and thousands injured after their pagers, sourced from a Taiwanese manufacturer and allegedly tampered with during the supply chain process, detonated.
Cybersecurity expert Abhirup Guha emphasizes that this incident is a watershed moment in the realm of cyberattacks, marking a troubling shift from traditional data theft to direct physical harm. The suspected infiltration of these pagers, likely facilitated by hostile state actors, underscores the severe implications of supply chain vulnerabilities. Attackers may have implanted hidden explosive mechanisms or added backdoors in the firmware, enabling the remote activation of these deadly devices.
As the threat landscape continues to evolve, consumer electronics—from medical devices like pacemakers and insulin pumps to automated vehicles—are increasingly targeted by hackers. In fact, rigged pacemakers can change heart rates, and hacked insulin pumps could deliver fatal overdoses. Even smartwatches have seen battery overheating incidents, while drones can be hijacked for attacks on critical infrastructure.
Guha advocates for enhanced security measures, noting that rigorous vetting of suppliers and secure firmware updates are essential. He calls on governments to impose stricter regulations on devices that pose life-threatening risks to bolster consumer safety.
The need for collective action in fortifying cybersecurity across the board has never been more urgent. As this incident illustrates, compromised devices can indeed become instruments of terror, highlighting the critical necessity for robust protection against emerging cyber threats.


